
What this mod can do
- Reviewed at commit 75c837c, Nov 11, 2026
- Puts text in your prompt box, which can replace what you typed
- Sees each prompt you send and can change or drop it
- Sees each tool call before it runs and can block or change it
- Also uses prompt.mention and tool.describe{tool=Bash}, which this page doesn't describe yet
3 more things it can do
- Reads files
- Asks you questions
- Adds slash commands
Good to know (3)
- Secrets you give with /mask or <secret> are used without asking, except by MCP tools.
- Values printed in pieces, hashed or passed through a script are not caught.
- In claude -p nobody can approve, so detected secrets are denied.
Preview
Terminal
  ⎿  secret-mask: secret-mask is hiding:
     {{SECRET_1:github-token}}  asks before use
Claude Desktop
Draws nothing in Claude Desktop.
What it does
In the author's words
Swaps secrets for placeholders before they reach the model, and puts them back only when a tool call you approve runs.
- What you see
- Approval prompts and a /mask input pane
- Works in
- Terminal
- Slash commands
- /mask, /secrets
- Uses your tokens
- No
- Changes files
- Nothing
- Network access
- None
- Reviewed commit
- 75c837c on Nov 11, 2026
- Preview recorded with
- Claude Code 2.1.309
How it works
- At session start, masks secret values in .env files up to three folders deep
- Swaps known token formats in your prompts and tool output for numbered placeholders
- Asks before a Bash, Edit, Write, WebFetch URL or MCP call fills in a detected secret
- /mask hands over a secret without asking later; /secrets lists the placeholders
Common questions
How do I stop Claude Code from reading the secrets in my .env files?
With this mod installed, values in .env* files up to three folders below the project root are masked from session start and again whenever Claude reads one. Keys like *_TOKEN, *_PASSWORD and *_SECRET are masked, while booleans, numbers, short plain words, paths and host names such as PORT=3000 stay readable. .env.example files are skipped.
Can Claude still use a token it cannot see?
Yes. Claude writes the placeholder, such as {{SECRET_1:github-token}}, into a Bash command, an Edit or Write, a WebFetch URL or MCP tool arguments. The mod asks you first, then puts the real value in right before the tool runs, and masks the output again on the way back. Text sent to a subagent or another model never gets the real value.
Does it catch secrets that are base64 or hex encoded?
Base64, base64url, hex, reversed and URL-encoded copies of a known value are masked in output, as markers that can never be unmasked. Values printed in pieces, hashed or run through a custom script are not caught, so the approval prompt is the real guard.
Badge for your README
Own this listing? Add it to your README. The badge shows the install count as it grows.
[](https://statuslin.es/mods/secret-mask?utm_source=readme-badge)
Or show the preview card:
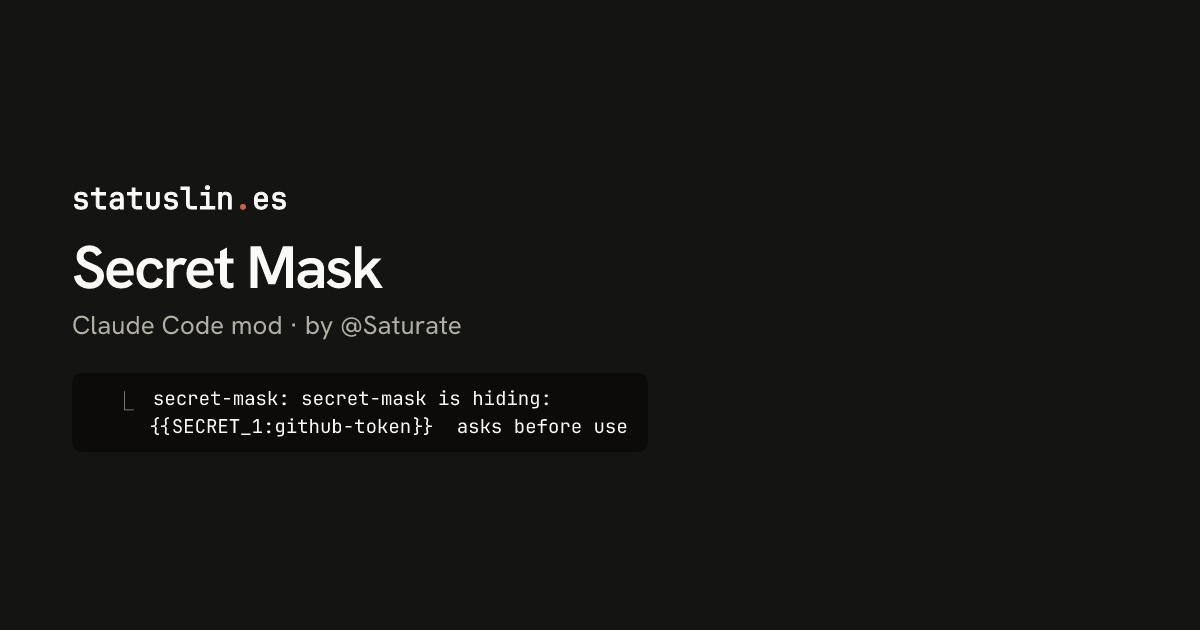
[](https://statuslin.es/mods/secret-mask?utm_source=readme-badge)